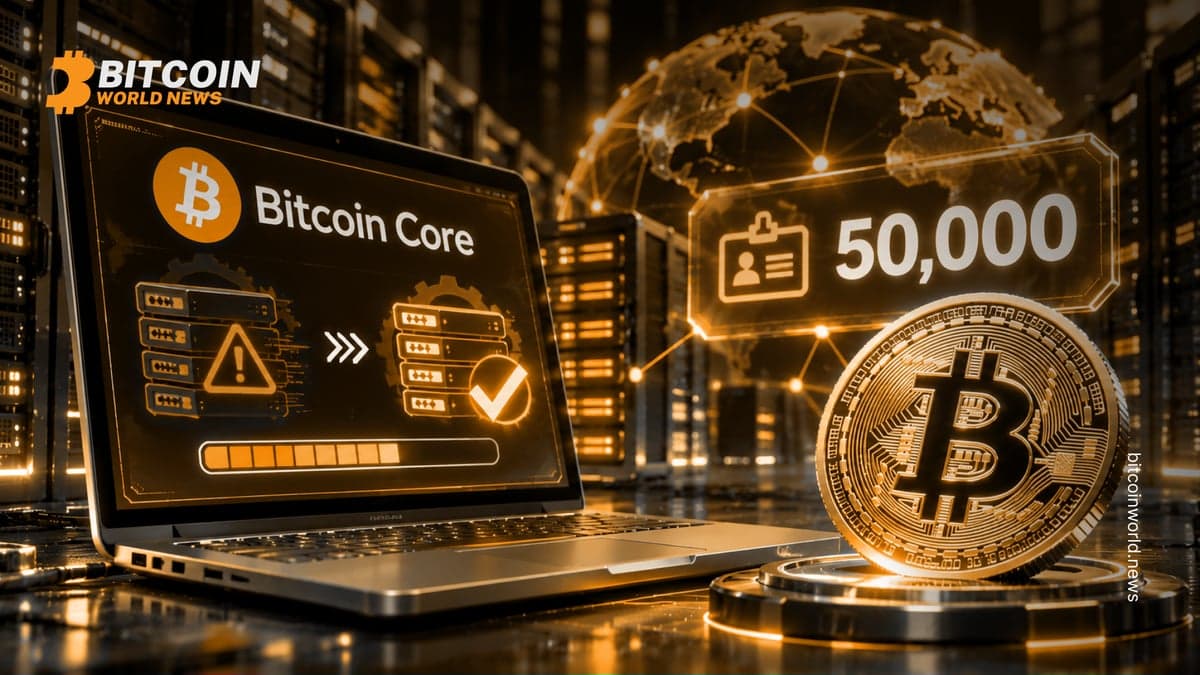
Bitcoin Core shipped fixes on Friday for a vulnerability that could stall Bitcoin (BTC) nodes by repeatedly submitting a single identifier 50,000 times. The issue was flagged by Loupe, an open-source scanner from Block’s Spiral that uses AI agents to examine Bitcoin code.
The patch closes off an attack path that could have degraded node responsiveness rather than compromising funds. While the bug centered on the handling of one repeated ID, it highlights how input validation paths in widely deployed cryptocurrency software must be hardened against pathological cases.
What did Bitcoin Core fix and why does it matter?
Developers patched a flaw where repeating one ID 50,000 times could stall Bitcoin nodes, restoring expected resiliency under adversarial traffic. It matters because node availability underpins the health of the Bitcoin network; stalling nodes can slow message propagation, disrupt peer connectivity, and erode service reliability for applications built on top.
The fix reduces exposure to resource exhaustion caused by malformed or repetitive inputs. Even without direct financial loss, degraded node performance can impair synchronization and transaction relay for wallets, exchanges, and data services that rely on steady peer-to-peer connectivity across the Bitcoin network.
How was the node-stalling bug discovered?
The flaw was identified by Loupe, an open-source scanning tool from Block’s Spiral that employs AI agents to review Bitcoin code. Loupe surfaced the repeated-ID edge case, enabling maintainers to ship targeted fixes on Friday. The find underscores a growing role for automated analysis to augment human review in critical cryptocurrency infrastructure.
By programmatically exploring code paths and stress conditions, AI-assisted scanners can surface high-impact denial-of-service vectors earlier, tightening feedback loops between discovery and remediation. That complements traditional peer review and test coverage, especially for complex networking and validation logic in Bitcoin Core.
What should node operators watch next?
With fixes shipped on Friday, the immediate exposure from this repeated-ID pathway is reduced, and operators should expect improved resilience under hostile inputs. The broader takeaway is that AI-driven auditing like Loupe’s will likely continue to surface edge cases, reinforcing the importance of timely patch adoption and ongoing code health monitoring.
The episode reinforces a defensive posture for Bitcoin infrastructure: rapid identification, disclosure, and remediation of performance-degrading vectors that target node stability rather than consensus rules. As automated tooling expands, similar hardening opportunities may emerge across networking, mempool handling, and message parsing layers.